Wednesday, August 21, 2013

How To Teach Science - What Is a Flame?


This animation was award winning and is the perfect demonstration on taking what appears to be a simple topic, but is actually quite complex, breaking it down, and teaching it in such a way that it is understandable:


Sunday, August 18, 2013

30 Year Wedding Anniversary in Maui


We celebrated our 30 Year Wedding Anniversary in Maui at Kaanapali Beach which was voted the best beach in the world for 2013.

Below is my lovely bride of 30 years.  It was the perfect week.


This was the 180 degree view from our Lanai (balcony) at The Whaler in Kaanapali on the island of Maui.


We had everything that you could ask for within walking distance.


We had GREAT sunsets.  I was rather proud of myself for timing the two sailboats that were crossing just before sunset our last night in Maui on my Nikon Coolpix 9100S that I had keep rebooting because the software was acting stupid (of course) while we were there.  Note, pulling the battery and SD card out for 1/2 an hour is your best bet here to totally reboot.


You never know who you will meet.  Erik Spoelstra, head coach of the twice world champion Miami Heat was at the table next to us the first day with a nice young lady.  Very nice guy.  I told him that he was a young Phil Jackson - NBA coach with 11 rings as a Head Coach and 2 as a player.


We went snorkeling at Honolua Bay and then went for a sail on a multi-million catamaran.


You have to have a convertible in Maui.  An 8 cylinder is the way to go.  I learned the hard way the first time we went to Maui in 1989 when I had a four banger and it could not get past the diesel spewing bus in front of us on the way up to Haleakela - dormant volcano.

Below is a must in Maui - going to Lahina and having lunch at Cheese Burger in Paradise and having a few drinks.


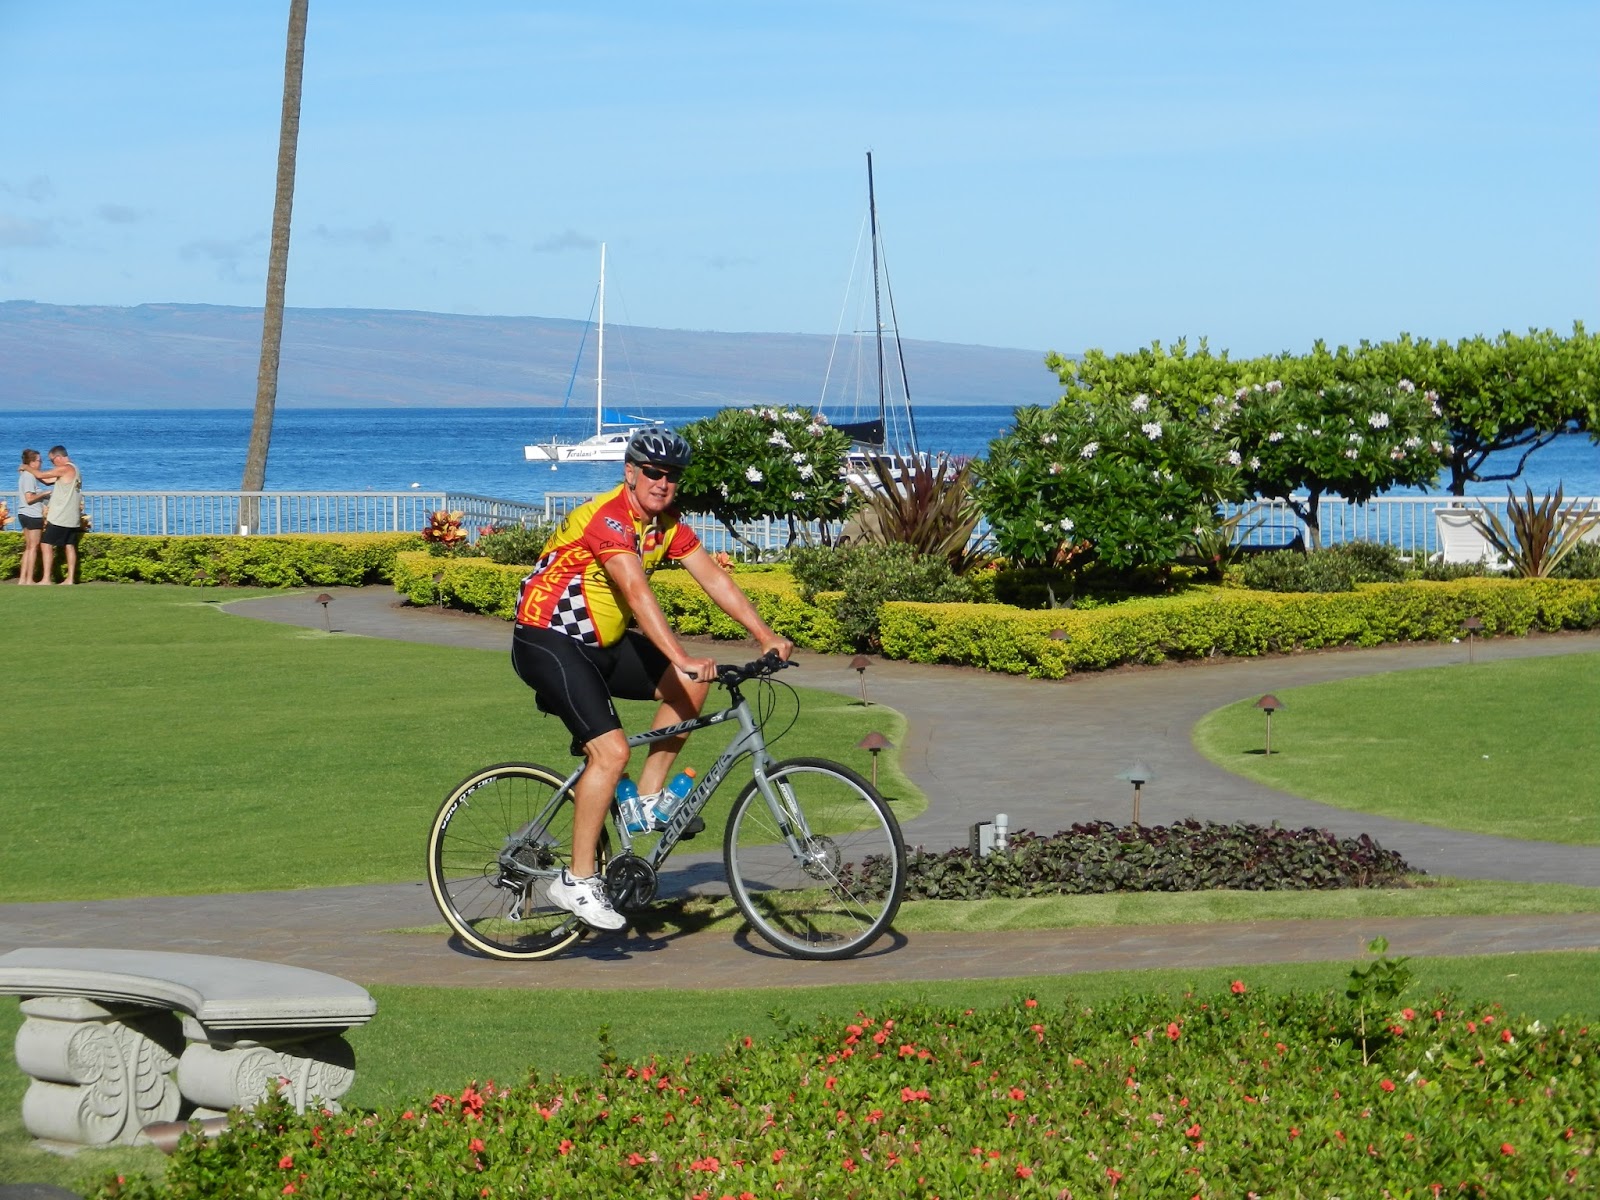
I rented a hybrid and went for a 25 mile bike ride one day.  Hard to beat the views in Maui.


At Black Rock at Kaanapali Beach the kids like to dive off the rocks.  I am sure if my boys would have come along, they would have been doing that as well.  Not me though - not even on a bet.


I went surfing for the first time.  It was a lot harder than I thought.  When we were in Waikiki in 2000, John and Michael were 12 and 10, they went surfing and did great.  Great being that got up every time and surfed all the way in after going 100 yards out.  One of the challenges was the reason the water was breaking where we were at was the coral.  They told us that when you fall off you must do a belly or back flop to make sure that you do not hit the coral that could be 2 to 3 feet below the surface.  With everything you need to remember in terms of getting up (either the pop method or the two step method), getting balanced, riding the waves, looking out for other surfers, worrying about the freaking coral was the last thing I wanted to worry about.  I did get slightly cut and bruised after two hours.  Was it worth it? Absolutely! 


We spent every day at the beach swimming.  Tough life :)

We visited our oldest son John and his girlfriend Janet on the way back.  Here we had lunch at Tony's Pizza Napoletana - best pizza in SF.


Below is Janet, John and Julie at Sutro Baths in SF.


Above we had a great dinner at Caffe Sport.  I was first introduced to this great restaurant back in the late 1980s by Neil Groundwater.  Prior to 9/11, Caffe Sport had three dinner seatings.  They stopped that practice after 9/11 because dinner traffic in general slowed down in the city.

Below is John and Janet in the Sutro Bath area with the Golden Gate bridge in the background.  Americas Cup was going on as well, which was interesting.


[MC]2 2013 Videos NOW Available!


Thanks to AMT's Diyana Hrzic for the GREAT JOB editing ALL of these videos and for Hilena Hailu for getting these organized and posted!

As is stated at the MTConnect Institute's homepage:

[MC]2 2013 Conference Presentations and Videos Released 

Logo MC2The second annual [MC]2 MTConnect: Connecting Manufacturing Conference was held in Cincinnati, OH on April 10-11, 2013. With over 150 attendees, the conference brought together an energetic and inspired group of manufacturers, developers, technology builders, and technology distributors.  It consisted of business and technical tracks, and provided an opportunity to learn from the experts to understand how this game-changing technology is making tremendous productivity gains in manufacturing.  The exhibits, birds of feather sessions, and receptions also gave attendees plenty of opportunities to network.
Visit the [MC]2 2013 page to download presentations and view videos from the conference.

Michael Edstrom's Internship at AMT - The Association For Manufacturing Technology


My middle son, Michael, worked this summer as an internship at AMT - The Association For Manufacturing Technology.  He worked in the Communications Department helping out reviewing and writing articles as well as helping out in a variety of other ways.  AMT is where I consult and is a fantastic organization.  Michael learned a ton and had a fantastic experience.  As a father, I could not have asked for a better experience for one of my sons.  Thanks to all the great folks at AMT for providing this opportunity to Michael this summer! 

Below is a picture of Michael and me on his last day this past Thursday August 15th, 2013.  I could not be more proud of Michael.  He graduates this December from Virginia Tech with two degrees in Professional Writing as well as Creative Writing.  He is going on for his Masters Degree in English in December at VT.


We commuted in together, so Michael had to listen to my radio choices.  He probably got his fill of 60s and 70s music, Howard Stern and NPR :)


Wednesday, August 14, 2013

Manufacturing Authentication and Authorization

By: Dave Edstrom
"On the Internet, nobody knows you're a dog." That’s the caption on a classic cartoon that was created by Peter Steiner and published 20 years ago by The New Yorker. This cartoon has one dog sitting on a chair and typing on a computer while speaking to a second dog that is sitting on the floor. Besides its humor, it also perfectly summarizes the problem with computer security. Specifically, how do you know a person is really who they say they are, and what exactly is that person allowed to do?
In the world of security, this is called authentication and authorization, which are two of the key pillars upon which applications and data depend for safe operations. Think this is just for computer geeks to know? Think again. Security in manufacturing is everyone’s job.
As a shop owner, or plant manager, there are two basics questions that you should ask:
  • Who and what have access to which systems in our plant?
  • Of these individuals and entities that have access to our plant, what are they allowed and notallowed to access and do?
If you or someone in your plant cannot answer these questions immediately, then your security measures could best be described as “crossing your fingers and hoping for the best.” This type of response is typically not a good idea in business. Those two questions fall into the high-level categories of computer security known as authentication and authorization.
Authentication is verifying that an entity (human or system) is who it really says it is, and authorization is what that entity is allowed to do. In the June 2013 edition of IMTS Insider, I wrote about cyber security and manufacturing, and in the July 2013 edition, I wrote about manufacturing passwords. In this round we will take a look at how authentication and authorization work together in manufacturing systems. Authorization is what these entities (human or system) are allowed to do and not do ¬¬¬¬ once you have verified their identities.
There is a misconception that if an individual has ‘password’ or the name of their pet as their password, that it only affects them and their account. The problem with this thinking is that it just takes one open account for the bad guys to get into your system. If you read about computer security break-ins, the scenario is typically the bad guys find a known vulnerability in the system and take advantage of it.
Instead of including a number of long paragraphs on authentication and authorization, I thought it might make more sense to first include a series of questions that should be answered. These are just a few and certainly not an exhaustive list:
  • Do you know everyone who has access to your systems?
  • What are your onboarding security procedures?
  • If an employee leaves, how quickly are they removed from all your systems? This can be a real issue. If you fire a poor performing employee and it takes two weeks to get them out of your system, that’s likely not a good scenario.
  • Is the access just a login name and a password, or is it multiple factor? In other words, if someone steals an employee’s login and password, can they get into your shop or plant, or do you have multiple-factor authentication in place? See my previous article in July 2013 on this topic.
  • Do employees have access remotely?
  • Are your passwords safe? In other words, how easily can the password be guessed or cracked by an intruder? How do you know? Have you run a password-guessing program on your system?
  • What systems have access to what other systems? If someone in the front office leaves his or her system open, could someone get access to the plant or shop floor?
  • Do you have a security firewall in place? Have you run a penetration test on your plant?
  • When employees login remotely, is there a requirement for the security on those machines?
  • Remember, a company’s biggest security holes are always people. If you change your passwords too often and the requirements are too severe, then employees start writing their passwords down and put them in a desk drawer. Or even better, they put a sticky note on their monitor. Take one guess how people find other employees’ passwords?
  • Do you provide access to your suppliers?
  • How does your company protect itself and its employees from viruses, worms, spyware, malware and the plethora of bad software that wants to infect, take over and do havoc on systems?
  • Who has access to equipment on the shop floor?
  • Do you have a network monitoring system?
  • Do you have log files on who is coming and going electronically? Is there a reason an employee should be logging in at 11:30pm on a Friday night?
  • Do you have a remote monitoring system? How is that secured? Is everything encrypted?
  • Do you keep all of your operating system updates current? How about your applications or plugins?
  • If you use Java, is that current? Do you keep older versions of Java around when you don’t need to?
  • Do you have an access control list?
  • How are security policies defined?
  • Is file sharing enabled? How is security handled?
  • Is your Wi-Fi wide open with no security? What security are you using for Wi-Fi? Some systems are easily breakable.
  • When was the last time you spoke to your employees about plant cyber security?
  • If your system was compromised with a security breach, what would you do?
  • Do you have a backup in the cloud if all your systems and the backups were compromised?
  • Most importantly, who is responsible for your shop or plant’s security?
You need to be as serious as a heart attack about protecting your plant or shop’s computer security. If you think you’re too busy to worry about security, then pay someone to come in and do a security assessment.
The only way you can be absolutely sure that you are safe when it comes to cyber security is to not use anything that has a processor or a connection. Unfortunately, that’s not an option for most manufacturers on this planet.
Think about security the same way the Secret Service thinks about protecting the President of the United States – a series of layers with multiple contingency plans. The great folks at the Secret Service ask a couple of simple but very difficult questions:
  • Can we protect the President in this physical location? If the answer is yes, then a detailed plan is put together on how.
  • Second: If something bad happens with the president here, can we secure the area, or do we have to get the President out of here immediately? If the answer is to get out, then a series of options are exercised to determine where and how.
Since abandoning your shop or plant on a cyber security breach is a non-option, then careful planning is your only real course of action. Maybe there needs to be a cartoon showing bots flying around the shop floor on networking cables, stealing parts programs and with the caption, “why do we need to create new designs, when we can just as easily steal them?”
The sad part is that this scenario is real today and it is certainly not funny. Just as protecting the President of the United States is not 100% risk free; neither is protecting your shop or plant from a security breach. The key is to plan with experts, constantly monitor and then continue to update your plans.
Next month, I will continue my series in the IMTS Insider on manufacturing cyber security by discussing Manufacturing Encryption. Just as a reminder, I am just touching on the absolute tip of the iceberg in these series of articles, so if you are not sure about your security practices, please hire a security consultant. Please keep your comments and suggestions coming!

You can place a question here by simply hitting the comment button!

Monday, July 29, 2013

Mazak MTConnect Enables Florence, Kentucky Plant


This is REALLY big news!  This is a great news for Mazak and MTConnect!  

Here are some snippets from the press release.

"In implementing the protocol into the Kentucky operations, Mazak continues its MTConnect leadership and demonstrates its commitment to the protocol as a powerful tool for all manufacturers to improve productivity, machine utilization and efficiency. Mazak has been an ardent supporter of MTConnect since its inception, offering all its machines with MTConnect compatibility. Currently, over 100 Mazak customers are at various stages of MTConnect integration within their own facilities involving approximately 300 machines within a wide range of model types."

“We continue to take a leadership position in propagating the MTConnect open protocol,” said Brian Papke, president of Mazak Corporation. “MTConnect’s value to our customers is in the ability for them to establish extensive and open channels of communication for plug-and-play interconnectivity between devices. MTConnect allows software to be universally applied between different types of machine models so that information is readily available for improving machine tool utilization. Using this capability, Mazak is taking another positive step in further increasing the productivity of our North American operations and ensuring the strong competitiveness of our
Kentucky manufacturing.”
 "According to Neil Desrosiers, Mazak’s developer of digital solutions, the full improvement potential resulting from MTConnect at the Kentucky plant will be achieved when the measurement data is collected and full potential machine tool utilization is realized in the factory."

Canadian Industrial Machinery Article - The Internet Comes to Manufacturing


Joe Thompson wrote a great article for Canadian Industrial Machinery that was titled:

The Internet Comes to Manufacturing

The digital age has arrived on the shop floor, increasing process speed, reducing nonproductive time.
Joe starts off the article with, "If data is being collected, then it should be used. And, once again,new technology enables this."

Dave Edstrom

Joe goes on to say, "Imagine anywhere, anytime access to all facets of your manufacturing process."
Edstrom also is the author of MTConnect: To Measure Is To Know, a book that addresses how open-source, royalty-free standards systems can revolutionize the business of manufacturing.

Cloud computing has potential to be game-changing technology in manufacturing for everyone from small shops to extremely large manufacturing plants. The key is understanding the process, asking the right questions, and making wise decisions.

“Cloud computing is important for manufacturing because it allows companies to avoid the countless business and technical issues associated with running their own data centers and save money by paying only for the computing resources when they need it on a pay-as-you-go model,” said Edstrom."

Friday, July 26, 2013

President of Network Appliance's Complacency Kills Article


There is a great article at Forbes titled, Complacency Kills, on how big companies die.  It is written by Tom Mendoza, president of NetApps at Forbes.  Having lots of former Sun Microsystems employees at NetApps, I know for a fact they do truly care about culture and their employees.

Here is a snippet:

"Here’s how to recognize complacency and fight it.

In the 1980′s, Digital Equipment was a powerhouse, seemingly unstoppable. But Digital got complacent. It failed to respond to technological changes—and it was gone in ten years.
In 2000, what would you have bet that Sun Microsystems would still be in business by 2010? It would have been a bad bet. Sun was on top of the world then, but by 2008, its stock had lost 80% of its value and it disappeared the next year. Sun’s sprawling corporate headquarters now houses Facebook.
These and other companies failed for many reasons, but complacency was front and center. Why didn’t they do something about it?"

75 Mile Bike Ride


Yesterday was a picture perfect day for a bike ride that started out 20 miles with my wife Julie and ended up being a 75 mile ride.  Julie and I rode together from Leesburg to Purcelleville and back (20 miles total).  This is all part of prep for the Seagull Century that I ride in every October with long time friend Jeff Stone.

Below was my speedometer.


Wednesday, July 17, 2013

Sun Founder's The Computer History Museum


Today is the SunDC Sun Microsytems Reunion at Coastal Flats.  Here is the video on the Computer History Museum that was the founders of Sun talking about Sun's history.  I was there in the 3rd row.  I asked Bill Joy and John Gage to retell the "Network Is The Computer Story" which I heard both Bill and John tell me on separate occasions when were having dinner together in Aspen and Georgetown repsectively.  It was a great night listening to Andy Bechtolscheim, Vinod Khosla, Scott McNealy and Bill Joy.


In the photo above, I asked Bill Joy to retell the story of how "The Network Is The Computer", which came about at the 1:43:40 mark in the video below:


Sunday, July 14, 2013

Great Week in Ocean City, Maryland with the Franklins of Marshall, Wisconsin


Julie and I spent a week in Ocean City, Maryland with Bobbi and Richard Franklin (my cousin) of Marshall, Wisconsin as well as their daughter Tayor and Taylor's friend Kimberly.   Below are some of the highlights.


The first mandatory health stop if to Thrasher for their world famous boardwalk french fries with vinegar - NO KETCHUP as they like to say :-)

Early morning view from out balcony of the three umbrellas and four chairs I set up at 7:30am every morning.


Little blurry, but they showed movies on the beach in front of our condo.

Bobbi Franklin and Julie


Taylor Franklin and her friend Kimberly.


Julie and me at our new favorite restaurant in Ocean City - the Harborside Bar and Grill which are known for their orange crushes.  You have to like any restaurant that has a sign the "bikers can not wear their colors".   They are not talking about your Lance Armstrong Trek jersey either.


Above is the orange crush from the Crabcake Factory which Julie and I ate at twice since it was just one block from our condo on the ocean side.

Richard and I like to compete on everything.  Below is me kicking his butt boogie boarding! :-)


One of the highlights was the 46.2 round trip Ocean City to Rehoboth bike ride that my cousin Richard and I took one day.  We had a 16 to 20mph southerly tailwind, so we flew up there.  Not so easy on the way back.  This was a distance record for Richard.  It was also tough because he broke a spoke and the bike shop in Bethany did not line the rear tire up correctly when they fixed his spoke on the way back, so his brake was rubbing all the way from Bethany to OC and we did not realize this until we got to OC.


Some fireworks on the 4th of July.  We sat out in front of Bobbi and Richard's tennis courts to have a great view on  a perfect night.


Robot Operating System (ROS) and MTConnect Video


This is a great 8 minute video Robot Operating System (ROS) and MTConnect video that demonstrates how two open systems can work together to change everything you know about manufacturing.  This is a game-changer...


Saturday, July 13, 2013

MTConnect Challenge Phase II


This is an excellent video on the MTConnect Challenge 2.

As stated at the site:

"The MTConnect Challenge seeks to engage and stimulate development of a broader base of advanced manufacturing intelligence software applications that acquire data utilizing the MTConnect standard. The intent is to enable a more efficient and competitive domestic manufacturing infrastructure for parts and assemblies for the defense enterprise. Additionally, the objective of this Challenge is to create valuable low cost software tools and applications that can be easily adopted by manufacturing enterprises, especially the mid and lower tier producers which represent a significant portion of the Department of Defense (DoD) supply chain, to enhance their manufacturing capabilities to produce parts and assemblies.

This, the second phase of the Challenge (Challenge 2), is seeking the development of software applications that harness innovation and manufacturing intelligence breakthroughs that could benefit the DoD and their industrial manufacturing supply chain.  Three prizes totaling $225,000 will be awarded to the winning submittals in Challenge 2."


Friday, July 12, 2013

Tim Shinbara's "Living in a Cyber-Enabled World" July 2013 IMTS Insider Article


Tim Shinbara, Technical Director at AMT - The Association For Manufacturing Technology, wrote a great article on "Living in a Cyber-Enabled World" for the July 12th, IMTS Insider.

Below is a very interesting point that Tim brings out regarding infrastructure:
"Under Executive Order 13636, Improving Critical Infrastructure Cybersecurity, the National Institute of Standards and Technology has the responsibility to develop a voluntary framework – based on existing standards, guidelines, and practices – for reducing cyber risks to critical infrastructure. NIST is holding workshops around the nation to gather industrial input and provide updates to their efforts on the Cyber Security Framework. You can find out more by doing a search for “cyber framework” on the NIST website, NIST.gov."

Manufacturing Passwords


-By:  Dave Edstrom
The title “Manufacturing Passwords” can be thought of as a double entendre. It could discuss passwords in the area of manufacturing, or, alternately, creating passwords themselves. These are actually both important topics.
In the June 2013 edition of IMTS Insider, I wrote about cyber security and manufacturing. Continuing with that theme, this time around we’ll examine the topic of passwords and manufacturing.
As manufacturing becomes more and more interconnected with the outside world, the need for security will increase exponentially. Security can be thought of as an onion with different layers that are needed for protection. The only 100% secure system is one that is not on any network, sitting in an electromagnetically sealed room running on its own power source where no individuals can get to it. Even then, I would be reluctant to bet my last dollar that someone couldn’t figure out a way to break in. Unless that system was a black box with a fixed function, it would likely not be a very useful system. Being on a network and accepting risk is part of doing business today.
One of the simplest areas to protect is having a good password system in place for all users and services. When you type your password, you are going through an authentication process. By entering your login name and password, the system authenticates you and lets you in. We are all familiar with the requirement that some sites have for strong passwords. While we think it can be an inconvenience, this is really for our protection — it makes it more difficult to break into that password. The two most important aspects of strong passwords are the length as well as the types of characters, numbers, and special symbols used.
A strong password for a user would be something along the lines of a!&tR)^-n8@#&y\B. That password is 16 characters in length and has a variety of characters to it. The obvious challenge with that type of password is that it is hard for us humans to remember. The trick is having a password that a human can remember and makes it difficult for computers to guess by having that mix of characters and a long password. The time it takes for a computer to guess your password can easily be quantified. Let’s say that your password is “PeterIMTS”. I am sure that is not Peter Eelman’s password, but if it were, an offline attack using five servers that used a total of 25 Graphic Processing Units (GPU) that could guess Peter’s password in couple of hours. (The processors your kids use to run video games make great password crackers.) An offline attack is where the password file has been downloaded or stolen from a site and the bad guys just keep trying to break the passwords so they can get specific passwords for specific users. If we used those same 25 GPUs with the password of a!&tR)^-n8@#&y\B, it would take about one hundred billion centuries. You read that right, one hundred billion centuries. The age of the universe is about 13.77 billion years old, just in case you are worried it was not long enough or complicated enough. That is with today’s computers. Keep in mind that Moore’s Law tells us the speed of computers effectively doubles every 18 to 24 months.
A not-so-obvious point to understand here is that Peter’s password of PeterIMTS is not stored in some file that anyone can just open (if they stole the file) and simply read what it is. What happens is that when your password is entered, it goes through what is called a one-way mathematical algorithm where what comes out the other side is a very long and complicated set of characters. There are different mathematical algorithms that are used today. As a user, this is not your worry unless you find out that the bad guy has broken into your site and taken your password file. When that happens, the first thing users are typically told is to immediately change their passwords. If you ever find out a site is storing your passwords in clear text or “in the open,” run and don’t walk to get your valuable information off that site.
The first password of a!&tR)^-n8@#&y\B is too hard and PeterIMTS is too easy, so what is a good compromise? There are many strategies and this topic is as controversial as mixing both politics and religion. Whatever I point out for your consideration, it’s likely any number of security experts would suggest a different and possibly better way. I am offering a suggestion that I think is reasonable. It is just one suggestion. Keep in mind that the trick is both a variety of characters as well as the length of the password that causes these massive brute force attacks to take a long time.
Let’s go back to Peter and his password. Peter could use a technique called haystacks. A haystack basically means creating a bigger haystack for the bad guy to find your password. I first heard of this technique at a Sun conference years ago and then later on a podcast with Steve Gibson of Security Now on the This Week in Tech (TWiT) series of podcasts. There is lots of good information on this topic at TWiT.tv/sn. A haystack is basically padding a password with a string of special characters that you can remember that are a prefix or suffix or both to the site for which you want a secure password.
Let’s look at an example with Peter. Peter would pick a series of characters that he could remember. This might be 8Caps*MJ23$ Those 11 characters would then be added to any site that Peter would go to. Peter likes the Caps and the Bulls, so this might be a reasonable way to pad his passwords. For example, Peter goes to a site called Legendary Hockey Player Jerseys. They want a password. Creating a new password every time is a hassle and using the same password is simply not wise. In this case, Peter could have a policy that says he will grab the first character of whatever sites he goes to and pads it with his Peter only padding set of characters. The password would be LHPJ8Caps*MJ23$. Now using that same 25 GPU system, it would take about 500 million centuries to break it. Peter should be able sleep at night with that type of security. The key of course is that only Peter knows his private padding password. If Peter went to his Bank of America site, it might be BOA8Caps*MJ23$. It is also critical to not have the same password at more than one site. Obviously, if Peter had a sticky note on his monitor with 8Caps*MJ23$, that would be a security hole.
At one of my previous employers, we couldn’t get some of our sales reps to take password security seriously. The sales VP had the technical team pull down a password-guessing program and run it against our password file. The results of the cracked passwords were published to their peers and the offending sales reps with the results. The VP then gave the sales reps explicit instructions to change to a secure password NOW. Peer pressure can be a powerful force because it just takes one weak password to give the guys wearing black hats all the entry they need into the network.
I am sure some of you are thinking — “but that still isn’t secure, because what happens if someone finds out my password? They become me with just my login and password.” You are absolutely correct. What we have been talking about is single factor authentication. In others words, a password is something that you know. For systems where having just a login and password are not deemed enough, there is two-factor authentication.
Two-factor authentication adds another variable. For example, a company I worked at had a special password generator calculator, a device we called “the enigma,” and every employee that needed a remote login had one. It was unique for each employee. How it worked is that the employee would login to a special system with a unique login and an 8-digit challenge that they had one minute to reply to with their enigma response. For example, when I first turned on my enigma, I had to enter in my password and then immediately enter in the challenge. It would then come back with the unique number that I would have to enter into the system for that given one-minute window just for Dave Edstrom. If that was successful, I would then be asked which system I wanted to login to with my username and password. That was deemed as secure enough for our needs.
For other systems, even two-factor authentication isn’t enough, and a third factor is added. The third factor is something that you are. It might be a fingerprint or retina scan. In summary, a single factor authentication is typically something you know. A two-factor is usually something you know, as well as something you have, such as an enigma card. A third factor might add something like a retina scan.
Some might argue that authentication involving an enigma card and a fingerprint or retina scan is enough and would eliminate the need for a user to remember a password. Companies employ various levels of authentication depending on the system. In the long run, having humans pick and try to remember passwords is not a good idea. Many smartphone manufacturers are considering biometrics for the security systems on their devices.
If you have traveled recently, you likely noticed new traveler kiosks in some of the larger airports. These kiosks are part of a trusted traveler program. These programs go by different names around the globe, but the common theme is that it is for those travelers who have been deemed “safe” for air travel and not a terrorist threat. What these kiosks all share is a multi-factor authentication system. These multiple factors usually require that the traveler has a current passport, scanned at the kiosk, plus two-factor biometric scanning – such as finger print scan and facial recognition. They’re also required to enter their flight number. These multiple factors fall into something you have, which is your passport, something you are, which are the two biometrics, and finally a booked flight, which is the reason you are at the airport to begin with. All of these factors combined provide the airport and airline with a high degree of confidence that the person traveling is the person that has been previously checked out and is not considered a traveling risk. The background checks can be quite extensive, but the benefits are a more streamlined entry and exit process when traveling.
At this point, you should be asking what the security policies are regarding passwords in your manufacturing shop or plant. What would happen if you ran a password-guessing program? The degree of security needs to be balanced with the risk. For example, let’s say that you have a crossword program that requires a login and password to save your last game. You got it free at iTunes and there is no financial transaction involved, and the worst thing that could happen is a stranger could pick up from your last crossword puzzle. Let’s compare that to the login for your health provider where you have all of your family’s medical records. You likely would want a very secure password for this site. What would happen if a nation state decided to attack your company’s site because they just read you were the proud recipient of a new aerospace contract? Would you bet your company’s intellectual property on your current security system? Who makes that determination at your company?
Just as a reminder, you can get a Ph.D. in the area of cyber security, so please treat these articles as simply high-level guides on what to think about. It’s not meant to be an all-encompassing discussion of security best practices. My goal is to spark conversations in shops and plants regarding security, but I’m not providing a recommendation that works for all scenarios. If you now have more questions than answers, then I have done my job. Remember Andy Grove of Intel’s timeless advice, “only the paranoid survive.” When it comes to security, be very paranoid.
Next month, I will discuss authentication and authorization. Please keep the comments and suggestions coming on cyber security in manufacturing!